CCIT News and Notices

Microsoft removed Copilot from select Microsoft 365 apps

Microsoft has removed in-app Copilot access from Word, Excel, PowerPoint and OneNote for institutional licenses, which includes Clemson. 

Copilot is still available for University users through the Copilot AI companion webpage, the Copilot app and Microsoft Outlook and Teams. 

Clemson users with a paid Microsoft 365 Copilot license will keep full in-app Copilot access. The option to purchase a Copilot license will be added to the Clemson University Marketplace by May 2026. 

If you have questions, reach out to your area’s IT Consultant or contact CCIT. 

Microsoft 365 apps now require 2FA when logging in

CCIT is expanding two-factor authentication (2FA) to Microsoft 365 applications. As of Thursday, April 2, 2026, apps like Microsoft Outlook, Word and Excel may now prompt users to authenticate with two-factor authentication (2FA) after logging in with a Clemson username and password. This change is part of an ongoing effort to better protect Clemson accounts, personal information and systems from unauthorized access. 

Two-factor authentication methods like Duo Mobile are already widely used across many Clemson services, so most users should be familiar with this process. Expanding 2FA to more applications helps provide consistent, reliable protection across University systems.

New email digest helps review messages sent to Junk

Beginning Friday, April 3, 2026, the Office of Information Security will introduce a new email digest to help students, faculty and staff identify messages that were flagged as spam and moved to the Junk Email folder in Outlook. 

This new digest gives users added visibility into messages that may require review. If a legitimate email was moved to the Junk folder, users can move it back to the Inbox directly in Outlook without submitting an IT Help ticket. 

A screenshot of the Daily Email Digest email that shows spam emails received.

This notification is separate from Microsoft’s existing quarantine emails. Microsoft notifications apply only to quarantined messages, while the new Clemson digest applies to potential spam messages routed to Junk. 

Users will only receive this new digest on days when one or more messages have been moved to their Junk folder. This added notice is intended to reduce the chance that a relevant email is missed because it was automatically sent to the Junk folder. 

New process for adding printing funds in PaperCut

With the upcoming end of the TigerStripe system, Clemson Computing and Information Technology (CCIT) is changing the way students add funds to their PaperCut printing accounts. Students who need to add printing funds beyond their semester quota will now use the TouchNet uPay system. 

Each student receives a printing quota of $25.50 per semester through Clemson’s PaperCut printing system. For most students, this quota is more than enough to cover their printing needs. Through May 31, PaperCut usage over this quota will continue to draw from any remaining TigerStripe balances. Students who still have a TigerStripe balance should use those funds before adding money through the new system.

To add printing funds, log in to the PaperCut web portal, click the Add Funds tab, select the amount you want to add and complete the steps on the TouchNet uPay payment page. After the transaction is finished, the PaperCut summary page will display the user’s updated printing balance.

Unlike the semester printing quota, added printing funds do not reset or expire, and any remaining balance will stay on the account until it is used. Because added funds are only used after the semester printing quota has been reached, students are encouraged to add only the amount they expect to need.

This change primarily affects students who print frequently or submit large posters to be plotted.

Beginning April 1, TigerStripe will no longer accept new deposits, and the service will be fully retired on June 1, 2026. Learn more about the sunsetting of the TigerStripe declining balance program on the TigerOne website. Questions about printing and plotting may be directed to the CCIT Support Center by emailing ithelp@clemson.edu, chatting online on TigerHub, or calling/texting (864) 656-3494.

IRS Scams

Because it is tax season, cybercriminals are increasing their use of Internal Revenue Service (IRS) themed scams.

These scams can include well-crafted phishing emails, text messages and phone calls. Cybercriminals are also using AI to create deepfakes, making their scam pitches even more believable. Other tactics include using social media to post fake content about false information, such as “secret refunds”.

As with most of these scams, their goal is to obtain personal information from you to use in their attack. Or they may try to solicit funds directly from you.

Please be aware that the IRS will never contact taxpayers directly by email, text messages or phone calls. Instead, they will contact you by letter sent through the U.S. Postal Service.

Hand holding a cell phone with text displaying on the phone saying "Scam! IRS calling".

Changes to Clemson Guest network

Beginning Thursday, February 26, 2026, at 4:30 p.m., the Office of Information Security will restrict access to certain apps and websites through the Clemson Guest network. The increased security measures will not impact users and devices connected to eduroam. This update is part of ongoing efforts to secure and safeguard Clemson’s networks and systems.

Additional apps will now require 2FA when logging in

CCIT is expanding two-factor authentication (2FA) to additional third-party applications. Some apps that did not previously require 2FA may now prompt users to authenticate after logging in with a Clemson username and password. This change is part of an ongoing effort to better protect Clemson accounts, personal information and systems from unauthorized access.

Two-factor authentication methods like Duo Mobile are already widely used across many Clemson services, so most users should be familiar with this process. Expanding 2FA to more applications helps provide consistent, reliable protection across University systems.

CCIT This Week: Update your Duo Mobile app before Feb. 2; beware of “browser in the browser” tricks; learn a new skill with Percipio

Week of January 26, 2025

Welcome to CCIT This Week, where we give you a rundown of news, events, tips and more. Follow us on social media for information and timely updates.


News

After February 2, the Duo Mobile app will not work for users who have not updated to version 4.85 or newer. Students, faculty and staff should ensure their app is up-to-date to avoid losing access to Clemson systems. Instructions to update your Duo Mobile app are available on the CCIT blog.


There has been an increase in cybercriminals using the Browser in the Browser (BitB) trick to steal login and password information. This trick has become more common on social media platforms such as Facebook and Instagram, but it can be used in any environment that uses a login page.


Events

Research, Computing and Data will host workshops this semester! Join the RCD team and expand your knowledge of high-performance computing and research resources available to you. The next workshop is “Introduction to Nextflow” on Tuesday, January 27 at 11 a.m. Registration is required; open to all Palmetto users.

The popular GIS Fundamentals Workshop Series continues this week! This 6-workshop series held on Friday mornings is streamlined to cover the GIS fundamentals; no prior experience is necessary. In-person sessions began January 16 or join online sessions starting February 27. Note: Attendance at the first two workshops is mandatory to participate in the remaining sessions.


January Tech Tip

A great New Year’s resolution: learn a new skill! Clemson faculty and staff have free access to Percipio, which offers thousands of courses, books, audiobooks and more to boost your professional development in a wide range of topics.

Keep Duo Mobile app updated to maintain access to Clemson systems 

Clemson University uses the Duo Mobile two-factor authentication (2FA) app to ensure security and privacy of University information and systems. Beginning February 2, Duo is ending support for older versions of the Duo Mobile app to improve security and performance. After this date, versions of the Duo Mobile app earlier than version 4.85 will not work to access Clemson University systems that require 2FA. 

Any app that is not updated by February 2 will lose the ability to authenticate and users will be locked out of Clemson services such as Canvas, iROAR, VPN and Kronos. 

To continue accessing Clemson systems that require 2FA, faculty, staff and students must update the Duo Mobile app or set up an alternate authentication method.

What to do:

  1. Check your device. Phone must meet these minimum requirements to support the latest version of Duo Mobile:
    • Apple devices: Go to Settings > General > About > iOS Version. Verify iOS 16 or higher.
    • Android devices: Go to Settings > About Phone > Android Version. Verify Android 11 or higher. 
  2. Update the Duo Mobile app. 

        If a phone can’t upgrade to at least iOS 16 or Android 11, other options are: 

        1. Using another smartphone or tablet that meets requirements for Duo Mobile. 
        2. Contacting the CCIT Support Center to discuss and set up other authentication options such as: 
          • Platform authenticators like Windows Hello or Apple TouchID 
          • Passkeys in password managers like Keeper, 1Password or Google Password Manager 
          • Hardware token ($20 cost) 

                Updating now ensures uninterrupted access to Clemson systems.  

                If faculty, staff or students have questions, need help updating or their device cannot be upgraded, visit the CCIT Support Center on the second floor of Cooper Library, email ithelp@clemson.edu or call (864) 656-3494. 

                Browser in the Browser (BitB) Trick

                There has been an increase in cybercriminals using the Browser in the Browser (BitB) trick to steal login and password information. This trick has become more common on social media platforms such as Facebook and Instagram, but it can be used in any environment that uses a login page.

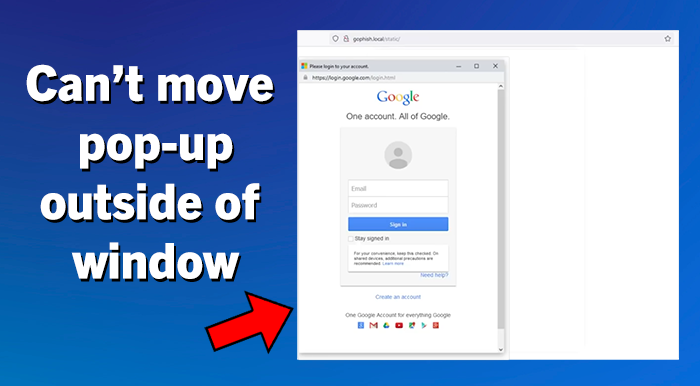
                The BitB trick uses hidden code to create a fake pop-up looking window in your browser with a login prompt. Because the fake pop-up is entirely generated, it can include a convincing-looking address bar at the top that displays correct domain names. This trick can easily fool users who are looking at the URL before entering their credentials. For example, the BitB trick could be showing what looks like a pop-up window for a Google login and include the correct google.com address as well as all of the correct graphics and formatting. After entering your credentials, the user may even be redirected and logged into the official website. But through this process, the cybercriminal also collected and saved the user’s login and password information, which they can use themselves later. Most login pages are static single pages and do not typically have their login screen in a pop-up window. One of the best ways to spot this BitB trick is that the pop-up window cannot be moved outside of the original main browser window.

                Image showing a pop-up window contained within a browser window and informational text saying "Can't move pop-up outside of window"

                Ways to Avoid the BitB trick:

                • For logging into any account, don’t trust a button, page link or email link.
                  Instead, navigate to the site’s official website URL in a separate browser tab to login.

                • If you are prompted to enter credentials into a login pop-up window, first check to see if the pop-up window can move outside of the browser window. Essential for the BitB trick, are iframes, which are connected to the underlying browser window and cannot be pulled outside it.

                • It is also recommended to use Two Factor Authentication on any account, when available, to give you an extra layer of protection.